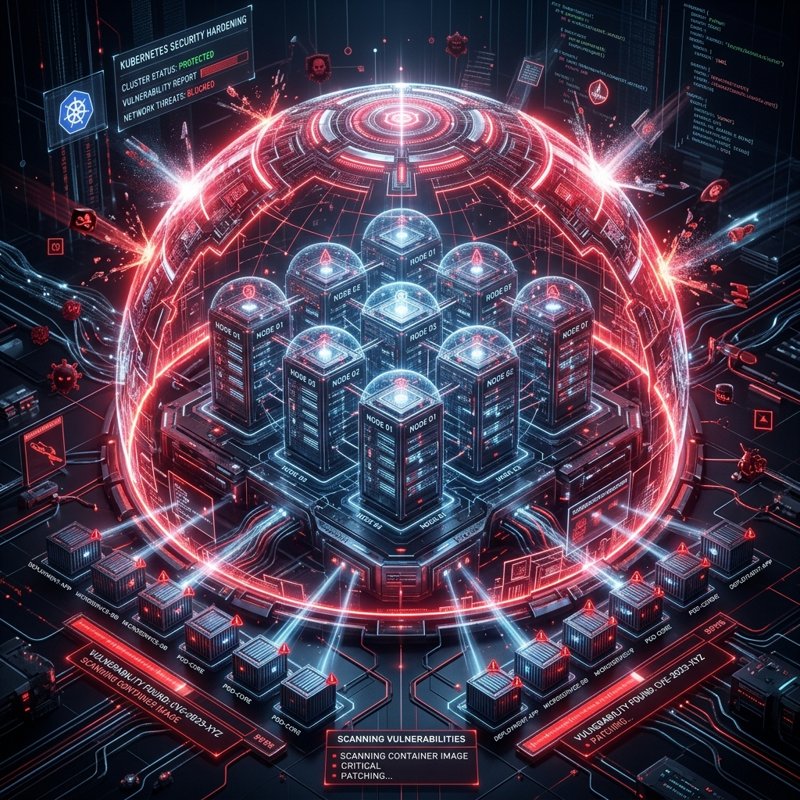
3 Layers of Cluster Hardening
Default Kubernetes setups allow unrestricted pod-to-pod network traffic and grant excessive ServiceAccount permissions. Passing enterprise B2B security questionnaires requires locking down cluster access boundaries.
- ▸Granular RBAC: Replacing cluster-admin bindings with scoped Roles and RoleBindings following the Principle of Least Privilege.
- ▸NetworkPolicies Namespace Isolation: Enforcing default-deny ingress and egress rules, explicitly whitelisting authorized inter-service communications.
- ▸Container Image Scanning: Integrating Trivy vulnerability scanning into CI/CD pipelines to block high/critical CVEs before container registry push.